Essential Eight Compliance Services Melbourne
Essential Eight assessment, implementation and maturity uplift for Australian SMEs, delivered by Melbourne-based engineers. Evidence in the format insurers, auditors and tender panels ask for.
Update, September 2026: ASD is consulting on replacing the Essential Eight with an Essentials series. The Essential Eight remains current and the guidance on this page still applies. Read what is changing and what to do now.
TechAssist assesses, implements and maintains the ASD Essential Eight for Australian SMEs, from Maturity Level 1 through to Maturity Level 3. You get a scored assessment across all eight strategies, a phased implementation plan, the engineering work to carry it out, and an evidence pack your insurer, auditor or tender panel can read. If you want the framework explained first, read our Essential Eight explained guide.
The service is for Melbourne and Australian businesses of 5 to 150 staff that need to show Essential Eight compliance rather than describe it: suppliers to Victorian and Commonwealth government, firms whose cyber insurance renewal now asks for maturity evidence, regulated industries with Privacy Act or sector obligations, and any SME whose customers have started sending security questionnaires.
What we assess: each of the eight strategies against the current ASD Essential Eight Maturity Model, with a Maturity Level 0 to 3 score per strategy and the gap to your target. What we implement: application control, patching for applications and operating systems, Microsoft Office macro restrictions, user application hardening, administrative privilege restriction, multi-factor authentication and tested backups, in the order that reduces your risk fastest. What you get: a written assessment, a staged roadmap, the controls deployed and tested, and documentation that is kept current as your environment changes. Melbourne-based engineers do the work, mostly remotely, with same-business-day on-site across Melbourne metro when a change needs hands on a device.
How Essential Eight Compliance Works
Three phases. Maturity Levels 0 to 3. Australian-based delivery.
01
Assess
Comprehensive maturity assessment across all eight strategies. We score your current Maturity Level (0-3) per strategy, document evidence, and identify which controls give you the fastest risk reduction for least effort.
02
Implement
Phased rollout to your target Maturity Level. Application control, patching, MFA, backups, implemented in the order that resolves your biggest risks first. Tested, documented, and aligned to your operational realities.
03
Maintain
Ongoing maturity monitoring, evidence documentation, control testing, and annual reassessment. Insurance-ready and audit-ready evidence packages. Your maturity doesn’t slip when staff change or platforms evolve.
The Eight Strategies
Each strategy addresses a specific class of cyber threat. Together they create layered defences that make attacks very difficult to succeed.
Maturity Levels 0, 1, 2, 3: What They Actually Mean
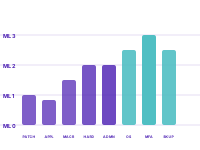
The Essential Eight uses a four-level maturity model. Most SMEs land at Maturity Level 0 or partial 1 when first assessed, not because they’re negligent, but because the framework’s specifics are exacting.
ML 0: weaknesses exploitable. ML 1, basic adversary defended (commodity ransomware, opportunistic phishing). ML 2, capable adversary defended (targeted attacks). ML 3, nation-state defended (rare for SMEs to need).
Most Melbourne SMEs target ML 1 as the baseline (sufficient for cyber insurance and most contractual requirements), with regulated industries pushing to ML 2.
Insurance, Audit and Compliance Use Cases
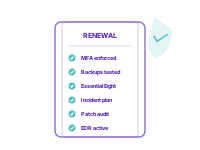
Essential Eight evidence is now standard at cyber insurance renewal. Underwriters specifically ask: which controls are in place, at what maturity level, with what documentation. The difference between approved-at-standard-premium and declined-or-loaded is often whether you can prove ML 1 across all eight strategies.
For government contractors (Commonwealth, Victorian state government, education sector), Essential Eight evidence is increasingly written into procurement requirements. For regulated industries (law firms with Privacy Act obligations, healthcare with My Health Record requirements, financial services with ASIC reporting), it overlaps with sector-specific compliance frameworks.
We produce the evidence package, control statements, test results, maturity scores, exception register, in the format insurers, auditors, and procurement officers expect.
Essential Eight Is the Floor, Not the Ceiling
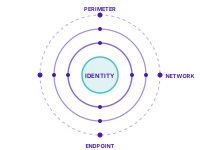
The Essential Eight is a baseline. Implementing it does not make you secure on its own. It addresses the techniques most commonly used in intrusions against Australian organisations. Targeted attacks, supply chain compromise and sophisticated social engineering still need defending.
For most SMEs, the right strategy is: get Essential Eight ML 1 in place properly first, then layer additional controls based on your specific threat profile. Our cybersecurity service extends the Essential Eight baseline with the additional controls your industry requires: 24/7 monitoring, incident response, penetration testing, threat intelligence.
How Long Does Essential Eight Compliance Take?
For a typical 30-100 staff Australian SME, getting to ML 1 across all eight strategies takes 3-6 months of phased implementation. ML 2 typically takes 6-12 months. The variables: how much existing infrastructure already aligns (often more than expected), how much legacy software you have (often less prepared for application control), and operational tolerance for change pace.
Most clients see meaningful risk reduction in the first month, even before formal ML 1 sign-off, because the highest-impact controls (MFA on internet-facing services, application allowlisting, daily backups) deliver outsized protection from minimal effort.
Benefits of Essential Eight Compliance with TechAssist
- Documented Maturity Score: Per-strategy maturity scoring, evidence-backed, ready for insurance and audit.
- Insurance Premium Reductions: Documented ML 1+ typically achieves better cyber insurance rates than competitors without it.
- Practical Implementation: Phased rollout aligned to your operations. Not a theoretical compliance exercise.
- Annual Reassessment: Maturity stays current as your environment evolves. Drift detected and remediated.
- Integrated with Managed IT: Implementation built into your managed IT service, not a separate engagement.
- Government Contractor Ready: Evidence packages aligned to Commonwealth, state, and local government procurement requirements.
Why Melbourne SMEs Choose TechAssist for Essential Eight
- Framework specialists: Engineers who’ve taken dozens of Melbourne SMEs from ML 0 to ML 1 and beyond.
- Over a decade of compliance experience across construction, manufacturing, logistics, law firms, mining, and professional services.
- ACSC-aligned methodology: Our assessments follow the official ASD/ACSC framework, not a vendor’s interpretation.
- Audit-ready evidence: Documentation in the format insurers, auditors, and government procurement officers expect.
- Phased implementation: Practical rollout sequences. We don’t break your operations to chase a compliance badge.
- Named clients trust us, StorageX, John Curtin & Associates, Magnium Australia.
Frequently asked questions
What is the Essential Eight?
Eight mitigation strategies published by the Australian Signals Directorate: patch applications, patch operating systems, multi-factor authentication, restrict administrative privileges, application control, restrict Microsoft Office macros, user application hardening, and regular backups. Together they address the large majority of the attack techniques that succeed against Australian organisations.
Is the Essential Eight mandatory?
It is mandatory for non-corporate Commonwealth entities. For private businesses it is not law, but it is increasingly a commercial requirement: insurers, enterprise customers and government tenders ask for it. Check the specific obligation that applies to you rather than assuming either way.
What do the maturity levels mean?
The ASD Essential Eight Maturity Model defines levels that step up in rigour, with each level describing what a more capable adversary would need to defeat. Most Australian SMEs are targeting the lower levels as a realistic baseline. We assess against the current published model rather than a remembered version of it, because the model is revised.
How long does an Essential Eight uplift take?
The assessment itself is short. The uplift depends almost entirely on how much legacy you are carrying: application control and administrative privilege restriction are the two that take real time in an established environment, because they change how people work. A staged roadmap over a few months is normal and preferable to a rushed rollout that gets reversed.
Can you provide evidence for an auditor or an insurer?
Yes. The output of an assessment is documented findings against each of the eight strategies with the current state, the gap and the remediation. That documentation is what an auditor, an insurer or a tender panel actually wants to see.
Ready to Make IT Your
Competitive Advantage?
Book a free consultation with our team. No pressure, no jargon, just a clear-eyed look at where you stand and what's possible.